Report suspicious guest invitations instead of just declining them!
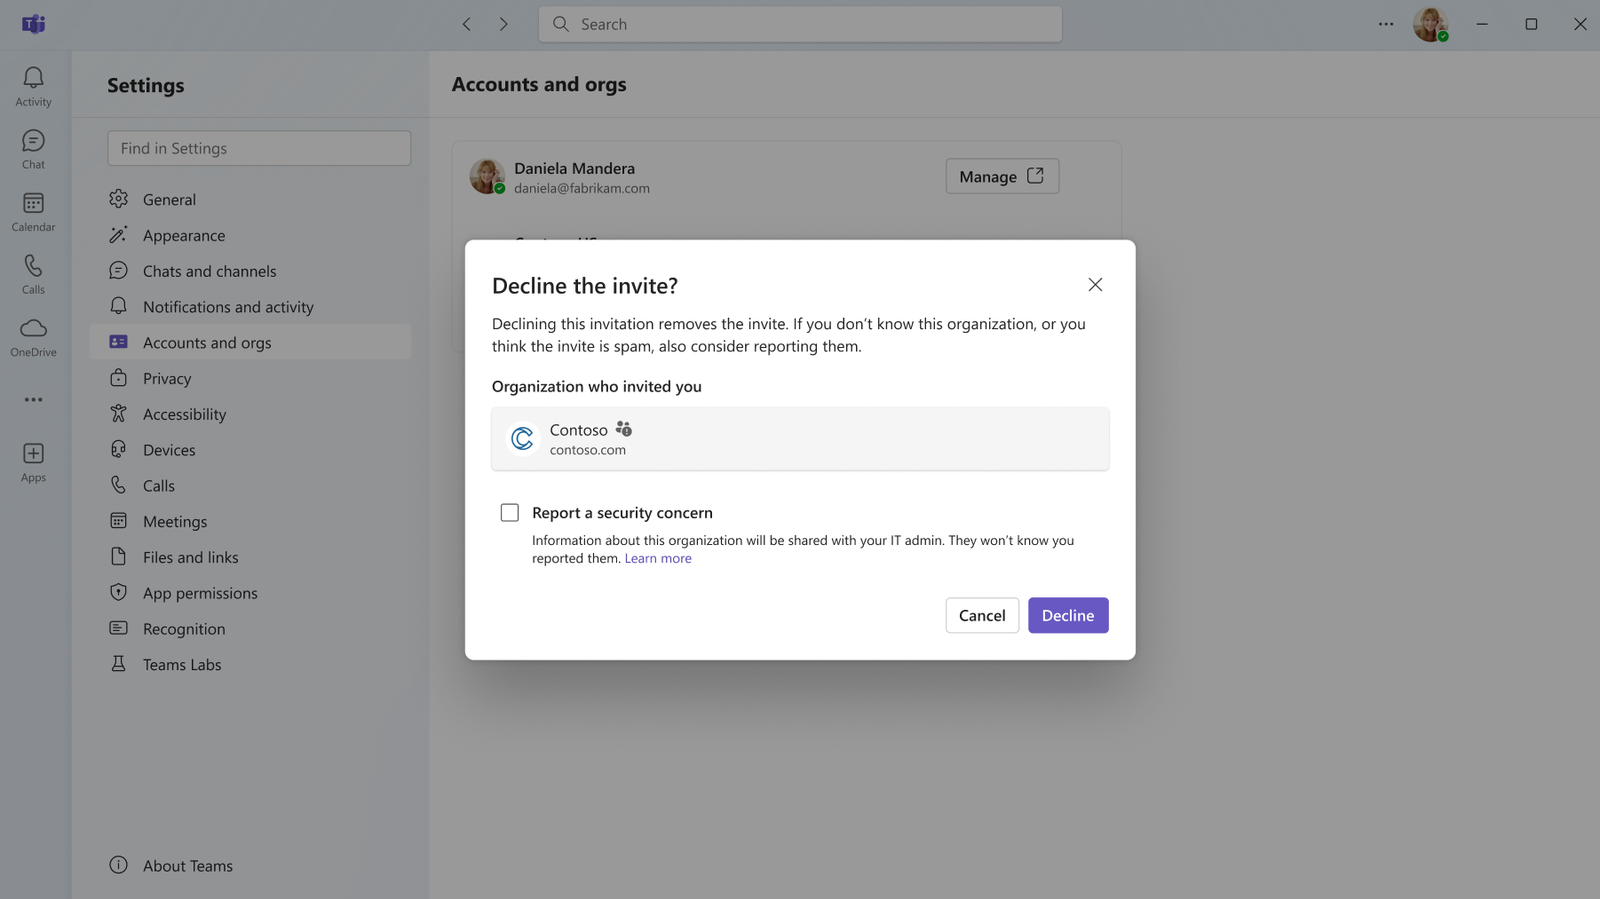
A foreign organization invites one of your employees as a guest, the employee declines, and your security team remains unaware. With MC1530615 (Roadmap 571297), Microsoft is adding a reporting option: If a user declines a guest invitation from another organization in Teams, they can now report it as suspicious.
What's new
The report is sent to two places. Microsoft receives it for review, and you’ll find it in the "User reported security submissions" report in the Teams Admin Center. This gives you the first insight into whether employees are receiving invitations that appear to be phishing attempts or abuse of the guest feature.
According to the Message Center, the feature will be available on Desktop, Mac, and Web. Rollout begins in early November 2026 and is expected to complete by mid-November 2026.
Why the signal was missing
A guest invitation is sent via Microsoft, which makes it appear trustworthy even if the inviting tenant is completely unknown to the recipient. Declining it protects the individual user but does not provide you with any information.
You only find out about a wave when someone calls the helpdesk. With the report in the Admin Center, you have a single place where multiple alerts for the same sender are displayed.
What you're checking now
This behavior depends on the "Report a security concern" setting in the Teams Messaging Policy. If it's already enabled for you, no action is required according to the Message Center.
There are two points you can clarify in advance.
First, the license: The entry does not specify any requirement. According to *Microsoft 365 for IT Pros 2027*, Microsoft requires Defender for Office 365 Plan 1 for reporting messages, but it is unconfirmed whether this also applies to guest invitations.
Second, the process: The book states that reported messages only appear in the Defender portal if reporting is also enabled there. If the Teams admin and security team are two different people, coordinate who reads the report.
Conclusion
This feature costs you almost nothing and closes a real gap in guest access: it turns a private rejection into a signal for your security team. Check the policy setting before the rollout in early November, clarify who is responsible for the report, and tell employees to report suspicious invitations instead of just dismissing them.
additional links
| Microsoft Message Center MC1530615 (Archive) | https://mc.merill.net/message/MC1530615 |
| Microsoft Roadmap RM571297 (Archive) | https://mc.merill.net/message/RM571297 |

💬 Comments
0 KommentareSei der Erste und starte die Diskussion mit einem hilfreichen Beitrag.
Leave a comment
Dein Beitrag wird vor der Veröffentlichung kurz geprüft — fachlich, respektvoll und auf den Punkt ist hier genau richtig.